
DevSecOps as a Service: Automated Security at Every Pipeline Stage — From Code Commit to Production


- Start with 30 Days Risk-Free Trial
- 24/7 Security Monitoring & Incident Response
Trusted by
Quick Actions:
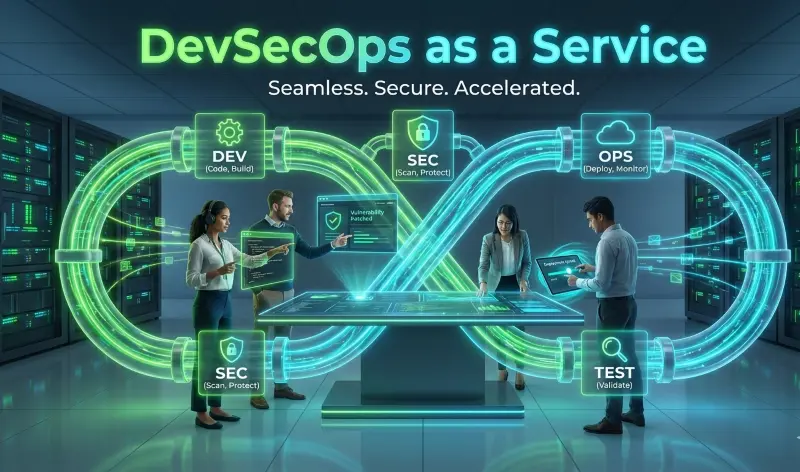
Transform Your Security Posture with Full-Stack Techies DevSecOps as a Service Solutions
Looking to catch vulnerabilities at code commit — not in production — and maintain continuous regulatory compliance without manual effort? Partner with Full-Stack Techies, a specialist DevSecOps as a service provider, for comprehensive DevSecOps solutions that integrate security seamlessly into every stage of your software delivery lifecycle.
Our DevSecOps services embed automated security testing — SAST, DAST, SCA, container image scanning, IaC security scanning, and runtime protection — directly into your CI/CD pipelines. Our certified security engineers bring 7–10 years of hands-on experience implementing shift-left security for cloud-native, Kubernetes-first organisations across AWS, Azure, GCP, Docker, Terraform, and GitLab. Every DevSecOps service engagement includes SOC 2, HIPAA, PCI DSS, and ISO 27001 compliance-as-code — enforced at every deployment, not just at audit time.
Verified Security Engineers
Sub-5 Min Security Scan
30-Day Risk-Free Trial
Why Choose Full-Stack Techies as Your
DevSecOps as a Service Provider?
Don’t settle for periodic security audits when you can access continuous, automated DevSecOps as a service from Full-Stack Techies. Our DevSecOps solutions are built on one principle: security should accelerate delivery, not block it. Our ISO-certified processes, AI-augmented vulnerability correlation, and comprehensive compliance-as-code coverage set us apart from typical DevSecOps services providers. Here is what makes us the trusted security engineering partner for 200+ organisations worldwide.

30-Day
Risk-Free Trial
Start with a 30-day trial to evaluate our DevSecOps as a service against your real pipelines and compliance requirements. You receive complete security tool configuration, full documentation, and all scanner integrations in your repository. Full refund if unsatisfied — no penalties, no questions, full handover regardless of outcome.

Top 3% Certified
DevSecOps Engineers
When you choose our DevSecOps as a service, you access the top 3% of global security engineering talent — only 3 out of 100 applicants qualify. Every DevSecOps service engineer holds active credentials including Kubernetes Security Specialist (CKS), CISSP, AWS Certified Security Specialty, Microsoft Certified Security Engineer, Snyk Certification, and HashiCorp Vault expertise.

AI-Augmented Vulnerability Correlation
Our DevSecOps solutions use AI-powered vulnerability correlation to eliminate duplicate findings across scanning tools and group related vulnerabilities into logical remediation batches — reducing remediation effort by 40–60%. Our AI tooling prioritises findings by business impact, not just CVSS score, so engineers fix what matters most first.

48-Hour Security
Team Deployment
Our DevSecOps as a service deploys certified security engineers to your environment in 48 hours. Basic implementation — SAST, SCA, and secrets detection in CI/CD — is live within 5–7 business days. A full DevSecOps managed services programme including container security, IaC scanning, runtime protection, and compliance-as-code is fully operational within 3–4 weeks.

Complete Compliance
Framework Coverage
Our DevSecOps managed services cover SOC 2 Type II (all five Trust Service Criteria), HIPAA Technical Safeguards, PCI DSS Requirements 6 and 11, ISO 27001 Annex A controls, and GDPR Article 32 technical measures — implemented as automated pipeline gates, not periodic audits. Audit preparation becomes a dashboard export.

Dedicated Security Project Manager — Free for Teams of 5+
Hire 5+ engineers for your DevSecOps as a service programme and receive a dedicated Security PM at no additional cost. Your PM coordinates security sprint planning, compliance roadmap tracking, stakeholder communication on security posture, and ensures on-time delivery of all DevSecOps service programme milestones.
Is Security Slowing Down Your Releases — or Worse, Missing Vulnerabilities Entirely?
The organisations that benefit most from DevSecOps as a service are not those with no security — they are those whose security practices cannot keep pace with their engineering velocity. These four problems represent the most common failure modes in modern application security programmes.
Manual Security Reviews Are Blocking Releases
by 2–6 Weeks
Traditional security processes — where a separate team manually reviews code, configurations, and containers before each release — add 2–6 weeks of delay per deployment cycle. Without automated DevSecOps services, security becomes a deployment gate, not a delivery enabler. Engineering teams resent delays; security teams are overwhelmed by review volumes that scale with deployment frequency.
As a result, security reviews become cursory, high-risk vulnerabilities slip through under schedule pressure, and the security function is perceived as an obstacle. This is the fundamental problem that DevSecOps as a service solves: security embedded in the pipeline and running in under 5 minutes — not layered on top and taking weeks to review.
⚠ Manual security reviews delay releases by 2–6 weeks per deployment cycle — Gartner Security & Risk Management Summit 2024.
Vulnerabilities Are Discovered in Production — After They Have Already Caused Damage
The average organisation discovers critical vulnerabilities 60–90 days after they are introduced into the codebase — typically through a production incident or third-party disclosure. Remediation then requires patching live systems, investigating breach exposure, notifying customers, and potentially engaging regulators.
The cost to remediate a vulnerability in production is 100× the cost to fix it in development. DevSecOps solutions that embed automated SAST, DAST, and container scanning directly into CI/CD pipelines catch vulnerabilities at code commit — where they are cheapest and fastest to fix, and before they ever reach a customer-facing environment.
⚠ Security breaches cost enterprises an average of $4.45 million per incident — IBM Cost of a Data Breach Report 2024.
Compliance with SOC 2, HIPAA, PCI DSS, and ISO 27001 Is Impossible to Maintain Manually
Regulatory compliance is a continuous state — not a periodic audit event. Yet most engineering teams manage it through manual evidence collection and frantic pre-audit preparation sprints. This approach fails completely at deployment velocities above one release per week.
45% of enterprises fail compliance audits due to inadequate or inconsistently enforced controls. DevSecOps managed services implement policy-as-code frameworks that enforce compliance requirements automatically at every deployment — generating audit-ready evidence as a natural by-product of CI/CD, not as a separate months-long preparation project.
⚠ 45% of enterprises fail compliance audits due to inadequate or inconsistently enforced controls — Ponemon Institute.
Container and Cloud-Native Security Is a Specialist Gap Most Teams Cannot Fill
Kubernetes, containerised microservices, and cloud-native architectures have fundamentally changed the security attack surface. Traditional perimeter security tools are insufficient for environments with hundreds of containers with dynamic IP addresses and ephemeral compute.
Container image vulnerabilities, misconfigured Kubernetes RBAC, exposed secrets in environment variables, and insecure service-to-service communication require specialist DevSecOps solutions to address. Most engineering teams lack deep expertise in Aqua Security, Trivy, Falco, or HashiCorp Vault — leaving cloud-native infrastructure with security gaps invisible to conventional scanners but well-known to adversaries.
⚠ Cloud-native environments introduce 5× more potential attack vectors than traditional infrastructure — CNCF Security White Paper.
How Full-Stack Techies DevSecOps as a Service
Solves Each Problem
Our DevSecOps as a service practice is built on one principle: security should accelerate delivery, not block it. Every DevSecOps solution catches vulnerabilities earlier, automates compliance evidence, and protects cloud-native infrastructure — without adding a single day of release delay.

Shift-Left Security Gates — Automated Scanning in Under 5 Minutes, Not 2–6 Weeks
Full-Stack Techies DevSecOps as a service embeds automated security at every pipeline stage: pre-commit hooks for secrets detection (git-secrets, TruffleHog); build-stage SAST (Snyk Code, SonarQube); pre-deployment DAST (OWASP ZAP, Burp Suite); and container image scanning (Trivy, Aqua Security). All scans complete in under 5 minutes — eliminating the review bottleneck entirely.
Security findings surface directly in developer tools — GitHub PR comments, GitLab annotations, Jira tickets — with CVSS scores and specific remediation guidance. Developers fix vulnerabilities in the same workflow where they write code. Our DevSecOps services clients consistently report deployments become more frequent after implementation, not less.
✓ Outcome: Security scanning in under 5 minutes. 2–6 week review bottleneck eliminated.

Continuous Vulnerability Management — Caught at Commit, Never in Production
Our DevSecOps solutions implement a continuous vulnerability management workflow tracking every finding from discovery to verified remediation. Critical vulnerabilities generate automated tickets with priority scoring, affected component mapping, and remediation playbooks in Jira, Linear, or Azure DevOps. Vulnerability trend dashboards provide real-time visibility into risk reduction velocity across your codebase.
Our AI-augmented correlation engine groups related vulnerabilities into logical remediation batches — reducing remediation effort by 40–60%. As a specialist DevSecOps service provider, we maintain all scanner signature databases and rule configurations — your team never manages scanner updates again.
✓ Outcome: Every vulnerability tracked, prioritised, and remediated. Zero unmanaged findings in production.

Compliance-as-Code — SOC 2, HIPAA, PCI DSS, ISO 27001 as Automated Pipeline Gates
Our DevSecOps managed services implement your compliance frameworks as executable code. Open Policy Agent policies block non-compliant infrastructure changes. AWS Config Rules and Azure Policy continuously audit your live environment. HIPAA Technical Safeguards are enforced as automated gates covering encryption, access controls, audit logging, and transmission security.
Every check generates immutable evidence feeding directly into your audit reporting system. Our DevSecOps as a service clients reduce pre-audit preparation from 6–8 weeks to a single dashboard export. Monthly compliance posture reports with real-time control coverage and exception tracking.
✓ Outcome: Perpetually audit-ready — SOC 2, HIPAA, PCI DSS, ISO 27001 maintained automatically.
Cloud-Native Container Security — Kubernetes RBAC, Vault Secrets, Falco Runtime Protection
Our DevSecOps solutions cover container security end-to-end: Kubernetes RBAC policy design and enforcement, namespace isolation, network policy configuration, container image hardening with distroless principles, and runtime threat detection with Falco monitoring every container for unexpected system calls and privilege escalation.
HashiCorp Vault eliminates hardcoded credentials through dynamic secret generation, automatic 24-hour rotation, and least-privilege access policies. Our DevSecOps service engineers hold Kubernetes Security Specialist (CKS) certification alongside Aqua Security and Snyk expertise. Sub-5-minute detection-to-containment for runtime threats.
✓ Outcome: End-to-end container security — RBAC, secrets, network policies, runtime protection.
Explore Full-Stack Techies’ Complete
DevOps Engineering Services
DevSecOps as a service is one component of a complete DevOps engineering practice. Full-Stack Techies delivers the full spectrum of DevOps services — from infrastructure automation and managed operations to security, strategy, and specialist engineering talent. Explore our interconnected service portfolio.
DevOps
as a Service
CI/CD pipeline automation, infrastructure as code, container orchestration, and 24/7 monitoring delivered by the top 3% of certified DevOps engineers deployed in 48 hours. The foundation layer for organisations needing a complete, flexible DevOps capability without the 3–6 month in-house hiring timeline. Includes a 30-day risk-free trial.
Managed
DevOps Services
Complete infrastructure ownership with guaranteed SLAs — 99.9% uptime, sub-30-minute P1 MTTR, and 20–35% cloud cost reduction within 90 days. Full operational accountability including CI/CD management, cloud infrastructure, 24/7 on-call, compliance-as-code, and continuous FinOps. For engineering organisations ready to transfer full operational ownership to a certified specialist provider.
DevSecOps
as a Service
You are already here — automated SAST, DAST, container security, compliance-as-code, and runtime protection embedded in your CI/CD pipeline. DevSecOps services that run in under 5 minutes, not 2–6 weeks. For teams ready to make security a delivery accelerator rather than a deployment blocker. 30-day risk-free trial available.
DevOps
Consulting
Infrastructure strategy and transformation roadmap for organisations at the start of their DevOps journey or scaling to the next maturity level. Our certified DevOps consultants conduct a comprehensive infrastructure audit, identify CI/CD bottlenecks and cost inefficiencies, evaluate your existing toolchain, and deliver a prioritised transformation roadmap within 48 hours of assessment completion.

Hire DevOps
Engineers
Pre-vetted, certified DevOps engineers deployed in 48 hours to embed with your existing team. Active AWS, Azure, GCP, Kubernetes, Terraform, and security certifications. Flexible engagement terms — minimum one month, scale up or down with two weeks’ notice. For organisations needing expert DevOps capacity without a full managed service engagement.
Gartner Top 10 Strategic Predictions for 2021 and Beyond
- Digital Business
- Trends
- Live from #GartnerSYM
Programming Language Python & JavaScript will lead the roost


Voices of Trust: What Our Clients Say


Our Growing Ecosystem of Partners

How Full-Stack Techies Implements DevSecOps as a Service — From Assessment to Full Coverage in 3–4 Weeks
Our streamlined DevSecOps as a service implementation delivers measurable security improvements from week one. We implement highest-impact controls first, ensuring your pipelines remain fully operational throughout. Basic DevSecOps services — SAST, SCA, and secrets detection — are live in 5–7 business days. Full programme coverage is operational within 3–4 weeks.
Security Assessment & Pipeline Audit
Existing security tooling and coverage review
CI/CD pipeline security gap analysis
Container and Kubernetes security assessment
Compliance control coverage gap analysis (SOC 2 / HIPAA / PCI DSS / ISO 27001)
Security Toolchain Design & Prioritisation
We deliver a prioritised DevSecOps solutions implementation plan based on the assessment — tool selection aligned to your CI/CD platform and cloud environment.
Tool stack selection (Snyk, SonarQube, OWASP ZAP, Trivy, Falco, Vault)
Implementation sequence ordered by risk reduction impact
Compliance gap remediation roadmap by framework
Developer workflow integration design (GitHub / GitLab / Jira)
Phased Implementation — Highest Impact First
We implement DevSecOps as a service in three phases to deliver value quickly without disrupting delivery pipelines.
Phase 1 (Days 3–7): SAST, SCA, secrets detection in CI/CD
Phase 2 (Days 7–14): DAST, container image scanning, IaC security scanning
Phase 3 (Days 14–21): Vault secrets management, compliance-as-code, Falco runtime security
All pipelines remain operational throughout every phase
Ongoing Security Operations & Optimisation
Post-implementation, our DevSecOps managed services team manages scanner updates, tunes alert thresholds, reviews new CVE disclosures, and provides monthly security posture reporting.
Continuous scanner signature updates and rule maintenance
Monthly security posture and vulnerability trend reports
Quarterly security architecture reviews
Executive dashboard updates with risk reduction trajectory
What Makes Full-Stack Techies’ DevSecOps as a Service
Different from Others
At Full-Stack Techies, we go beyond traditional application security testing — we provide comprehensive DevSecOps as a service that makes security an intrinsic property of your software delivery pipeline. With a perfect blend of automation expertise, cloud-native security knowledge, and compliance engineering, our DevSecOps services ensure every commit, every container, and every infrastructure change meets your security and regulatory requirements — automatically, continuously, and in under 5 minutes. Our DevSecOps managed services clients never face another failed compliance audit.
Full Stack Techies |
Others |
|
|
No Billing Until Tangible Delivery We invoice only upon achieving clearly defined deliverables, ensuring you pay for actual results and reducing financial risk. |
||
|
Risk-Free Trial We offer a 30-day trial period, allowing you to assess quality and compatibility. |
||
|
Business Continuity at Our Cost We implement detailed continuity strategies without extra charges, ensuring uninterrupted operations during development or transition. |
View Our Comparison With Others
Full Stack Techies |
Others |
|
|
Free Security & Risk Assessment We provide thorough security evaluations to protect your digital assets, identifying and mitigating potential risks proactively. |
||
|
Lifetime Support Guarantee We offer ongoing support for the lifespan of the solutions implemented, ensuring long-term reliability and client satisfaction. |
||
|
Free Project Management For teams of 5+, we provide experienced project managers at no cost to drive project execution efficiently. |
||
|
Optimized Infrastructure Costs We perform regular audits to eliminate unused resources, reduce waste, and lower your overall infrastructure costs. |
||
|
In-House R&D Team Full-Stack Techies invests in an in-house research and innovation team dedicated to exploring emerging technologies like AI, Blockchain, Quantum computing, IOT, and more. |
||
|
Providing Industry Experts as Needed We allocate domain-specific experts to ensure high-quality problem solving and innovation for your project’s success. |
||
|
Custom Training on Demand We offer customized training sessions to upskill your team, ensuring smooth adoption and integration of new technologies into your existing workflows. |
||
|
AI-Augmented Development House By integrating advanced AI-driven processes, Full-Stack Techies significantly reduces costs, enhancing efficiency and profitability for your business. |
||
|
AI Enabled Rapid Prototyping & Iterative Development At Full-Stack Techies, we employ AI enabled rapid prototyping and iterative development methodologies to swiftly transform your ideas into functional prototypes. |
||
|
Customizable Solutions Understanding that each business has unique challenges, we offer tailored services designed to adapt to your specific operational and strategic requirements with the help of industry experts or consultants. |
||
|
Top 10% Talent Acquisition Our stringent selection process ensures that only the top 3 out of 1,000 applicants are onboarded, guaranteeing high-quality talent for your projects. |
||
|
No Hidden Costs Our clear and straightforward pricing structures ensure you understand costs upfront, avoiding unexpected expenses. |
||
|
Blended Rate Pricing Approach Our pricing model blends flexible resource rates to deliver transparent, predictable costs aligned with your project scope and budget. |
||
|
Scalability & Flexible Team Our solutions are designed to grow with your business, seamlessly adapting to increasing demands and ensuring long-term viability. |
||
|
Seamless Integration with Legacy Systems Our team specializes in modernizing and integrating existing legacy systems with new, advanced solutions. |
||
|
Seamless Communication with Daily/ Weekly/Monthly Meetings We offer daily, weekly, or monthly meetings—set during project initiation—to ensure clear, consistent updates aligned with your preferences and project needs. |
||
|
24×7 Global Availability Our developers are available around the clock, aligned with your project’s time zone and schedule. We ensure continuous support for your front-end development needs—minimizing downtime and maximizing efficiency, no matter where you are. |
||
|
Global Certifications & Compliance We are ISO 9001:2015 and ISO/IEC 27001, SOC 2, GDPR, and HIPAA certified—ensuring data security, quality, and trust. |
||
|
Productive & Innovative Culture We cultivate a collaborative culture where innovation thrives, and process improvement is a core principle. By continuously refining our workflows, we deliver smarter, faster, and higher-quality React JS development solutions—tailored precisely to your business needs. |
What Our Clients Say About Our DevSecOps as a Service
Real feedback from engineering and security leaders who experienced Full-Stack Techies DevSecOps as a service. Watch what our clients have said about security outcomes, compliance results, and working with our team. Full-Stack Techies guarantees the security and reliability of your infrastructure. All DevSecOps managed services are governed by leading international standards and the most advanced access controls and compliance frameworks available.


End-to-End Security & Quality.
AIMLEAP guarantees the security and reliability of customer data. Data is secured by leading international
standards and the most advanced custom permissions on the market.


Brilliant Minds
One of the main reasons why you should consider outsourcing a DOT NET Development Company is smart & experienced developers. Hiring a developer with the right skill set is a difficult task. So, why go through all the trouble of hiring an in-house Dot Net Developer, when you can simply outsource an entire dedicated team of brilliant minds from a trusted ASP.NET Development company to handle your project efficiently.
Committed To Deliver Quality
A DOT NET Development Company in India is committed to delivering solutions with utmost quality. They have highly knowledgeable & skilled Dot Net specialists who understand your requirements deeply and ensure high-quality results. A DOT NET Web Development Company hires the best talents from the industry to develop an application with accuracy to deliver a great user experience.
Timely Support & Assistance
Even if there are time-zone differences, a dedicated DOT NET Development Company provides timely support to the customer. Do you have anyone to provide you with technical support? What would you do if sudden technical issues appear in the app? During such situations, you need assistance and support from professionals with extraordinary technical skills and knowledge. A top ASP.NET Development company is equipped with all communication tools and channels to deliver 24×7 support to the customers.
No New Development Center Required
The tremendous advantage of working with a DOT NET Development Company is that you don’t need to make any kind of investment to build your own infrastructure. New equipment, advanced devices and the salaries of developers may greatly affect your budget. Instead of setting up your own development hub, outsource DOT NET Web Development Company that has qualified professionals and access to modern software and equipment to deliver responsible service.
Well-Versed With Tools & Technologies
A DOT NET Development Company works with hundreds of customers from different industries, so it’s obvious to have great knowledge of modern tools and technologies. The ASP.NET Development company houses skilled and experienced developers who use most of their time to learn new software and frameworks. They stay updated with the latest and trendiest technologies to ensure agility and precision within their service.
Concentrate on Business Expansion
Whether you lead a startup business or a well-established enterprise, you can’t waste your precious time handling the development process. By giving the responsibility of development to a trusted DOT NET Development Company, you’ll have plenty of time to focus on your core business objectives without any stress.
Cut Down The Development Cost
The cost of developing an application is lower if you work with a DOT NET Development Company in India. Payroll, workspace, equipment, daily amenities, and other extra employee benefits can add up extra expenses. Outsourcing a full-fledged ASP.NET Development company will help you save a lot of money which you can later use on the growth and development of your business.
Delivers Flexibility
Flexibility is the main reason why a business leader prefers to outsource DOT NET Development Company. The best team of developers, designers, and managers is deployed to develop a DOT NET app based on your budget and requirements. You are flexible to change your requirements without any issues when you work with a DOT NET Web Development Company.
A Prestigious DevSecOps as a Service Provider Building Secure, Compliant, Cloud-Native Applications for Enterprise-Grade Engineering Organisations



Accept Payment Your
Preferred Way
AIMLEAP accepts payment from a complete payments platform
with simple, pay-as-you-go pricing starting at

Frequently Asked Questions About DevSecOps as a Service
Get answers to common questions about our DevSecOps as a service, implementation process, security automation, compliance requirements, and pricing. Still have questions? Schedule a free consultation with our DevSecOps specialists.
Q1: What is DevSecOps as a Service?
Q2: What is the difference between DevOps and DevSecOps?
Q3: Which compliance frameworks do your DevSecOps managed services cover?
Answer: Our DevSecOps managed services cover SOC 2 Type II (all five Trust Service Criteria), HIPAA Technical Safeguards, PCI DSS Requirements 6 and 11, ISO 27001 Annex A controls, and GDPR Article 32 technical and organisational security measures. Compliance controls are implemented as policy-as-code in CI/CD pipelines, with automated evidence generation at every deployment. Audit preparation becomes a dashboard export — not a months-long manual exercise.
Q4: What security scanning tools do your DevSecOps services use?
Q5: How long does it take to implement DevSecOps as a Service?
Q6: Will DevSecOps slow down our deployment pipeline?
Q7: How does your DevSecOps service handle container and Kubernetes security?
Q8: How is DevSecOps as a Service priced?
Ready to Stop Discovering Vulnerabilities in Production
and Start Catching Them at Commit?
Join 200+ engineering organisations that have made security a delivery accelerator with Full-Stack Techies DevSecOps as a service. Start your 30-day risk-free trial today. No pitch. No obligation. Just clarity on whether — and how — we can secure your pipeline together.